Website Security

WordPress malware removal

Your site cleaned, the way in closed and the site protected so the infection does not come back. We keep a copy of everything we remove, so you can see exactly what was on your site.

Get help now See our work Fixed quote after a free call

What you get

  • Containment
  • Evidence
  • Full cleanup
  • Core check
  • Entry point
  • Credentials

Sound familiar?

  • Visitors are sent to spam, gambling or fake prize sites.
  • Google, your browser or your host warns that the site is dangerous.
  • Administrator accounts you did not create keep appearing.
  • Visitors are asked to press keys or paste a command to prove they are human.
  • You cleaned the site, and the malware came back.

What is included

  • Containment The malicious code stopped from running so visitors are protected while we work
  • Evidence A copy of every malicious file and database entry kept before removal
  • Full cleanup Files, database, users, plugins, themes, scheduled tasks and injected scripts
  • Core check WordPress core files compared with the official versions
  • Entry point How the attacker got in, found and closed
  • Credentials Passwords, application passwords and API keys rotated with you
  • Blacklist review A review requested from Google once the site is clean
  • A written report What we found, what we removed and what we changed

Not included

  • Rebuilding a site that cannot be recovered (quoted separately if it comes to that)
  • Ongoing monitoring after the cleanup, unless you add it

What we find on hacked WordPress sites

In the incidents we have cleaned up, the visible symptom was rarely the whole problem. Alongside the obvious malware we have found:

  • Hidden administrator accounts that do not show in the Users screen and recreate themselves when deleted.
  • Fake plugins with believable names that remove themselves from the Plugins list while they keep running.
  • Injected scripts in theme files, plugin templates and the database, often only shown to some visitors.
  • Fake browser checks that tell visitors to press a key combination or paste a command, which installs malware on their own computer.
  • Credential stealers that capture logins, and scheduled tasks that reinstall everything overnight.
  • Hidden spam links pushed off-screen inside page content, invisible to visitors and editors but read by search engines.

That last one is the case we wrote up in detail: how we removed a hidden SEO spam infection from BenchmarkTitle.net, from the page-builder forensics to the database cleanup and the compromised plugin that let it in.

A scan-and-delete cleanup misses most of this, which is why sites get reinfected.

Evidence first

Before anything is deleted, we keep a copy of it. You get a record of what was on the site, and nothing legitimate is lost because it was mistaken for malware.

Staying clean

After a cleanup we can keep watching the site with Guardian Shield Lite, the security plugin we built from these incidents. It blocks new code from running until it is approved and alerts us to new administrators, changed files and known malware.

How it works

  1. Tell us it is urgent

    Use the form and choose the urgent option, or call either office.

    From you: Hosting and WordPress access, or someone who can give it to us.
  2. Contain

    We stop the damage first, so visitors stop being redirected or attacked.

  3. Keep the evidence, then clean

    Everything malicious is copied, then removed from files and database, including accounts and plugins that hide themselves.

  4. Close the way in

    We find how the attacker got in and close it: an outdated plugin, a stolen password, a leftover account.

    From you: Hosting access logs, if your host provides them.
  5. Protect and report

    Credentials rotated, site hardened, a review requested from Google, and a written report for you.

    From you: Help changing passwords only you control.

What affects the price

Every project gets a fixed quote after a free call, so you know the total before anything starts. These are the things that move it.

  • How widespread the infection is
  • Number of sites on the hosting account
  • Whether the site is blacklisted
  • Whether you add ongoing monitoring

Where we have done this

Snowy Owl Sled Dog Tours and White Wolf Rafting
  • Service business
  • Website security
  • Malware removal

Malware removed and two sister tour company websites locked down

Challenge
In October 2023 visitors to the Snowy Owl Sled Dog Tours website started seeing spam pop-ups and redirects. The site also ran an outdated PHP version, an outdated theme and several unused plugins, and it had not been updated since it was built.
Result
The infection was removed and the way in closed within about two weeks of the first report. By 6 November 2023 both sites were fully updated and on PHP 8.2.
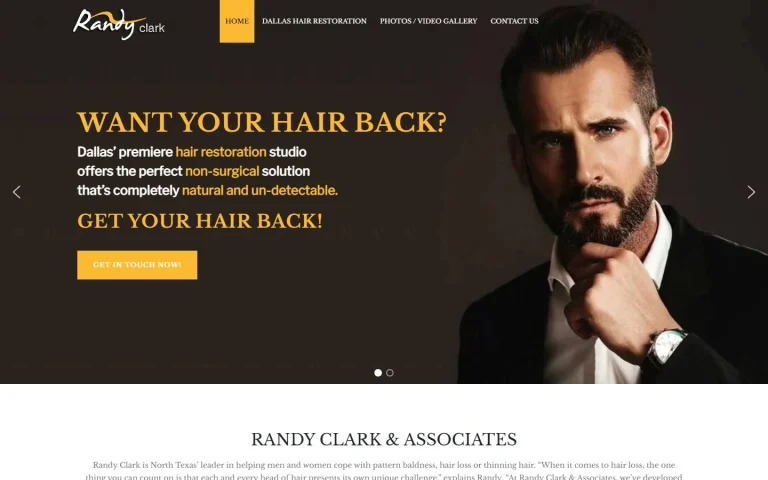
Randy Clark & Associates
  • Service business
  • WordPress
  • Speed optimization

Speed work, a rebuild and a malware cleanup for a hair replacement studio

Challenge
In September 2021 the studio's home page scored 13 out of 100 on Google PageSpeed mobile. The site also needed more and better images: the before and after photos were very low resolution.
Result
Google PageSpeed mobile went from 13 to 97 in September 2021, the rebuilt site went live on 25 May 2023, about seven weeks after kickoff, and Guardian Shield Lite removed the fake Cloudflare malware.
WordPress security plugin

Guardian Shield Lite

Our WordPress security plugin: code stays locked, known malware is removed with evidence kept, and every site reports to one hub.

  • Code locked, changes in recorded windows
  • Known malware removed, evidence kept
  • Every site watched from one hub

See all 4 case studies like these

Questions about WordPress malware removal.

What should I do before you start?

Change your hosting and WordPress passwords from a clean device. Do not delete files yourself yet: you may remove the evidence of how the attacker got in.

Will I lose content, orders or customer data?

We work to avoid it. We clean the infection out of your site rather than rolling everything back, and a copy of anything we remove is kept first.

How do I know it will not come back?

Reinfection usually happens because the way in was never closed. We find and close it, rotate passwords and keys, and can monitor the site afterwards.

Can you remove the Google warning?

Once the site is clean we request a review in Google Search Console. Google decides and sets the timing.

Do you clean sites for agencies, white-label?

Yes. We report to you, and you stay the contact for your client.

Tell us your goal. We'll show you the plan.

Book a free 30-minute call. You'll leave with a clear plan and a fixed quote, whether you hire us or not.

Book my free call
Free call, no obligationBook my call