WordPress security plugin by Codiffy

Guardian Shield Lite WordPress security built from real attacks.

Guardian Shield Lite locks your site's code, removes known malware only after saving the evidence, guards your administrator accounts and reports every site to a hub we watch.

  • Platform WordPress, with or without WooCommerce
  • Version 4.4.34, September 2026
  • How you get it With Codiffy security and maintenance
  • 15 minbetween the checks Guardian runs on every site
  • 5 minbetween front-page checks from the hub
  • 547malware signature strings in the current release
  • 30 daysof security activity in one plain-English report

Why we built it

Born in the middle of real attacks.

In 2026 we investigated and cleaned up attacks on WordPress and WooCommerce sites we look after. We found administrator accounts that came back after they were deleted, fake plugins that hid themselves from the Plugins screen, small web shells that rebuilt themselves on the next page view, credential stealers, and fake “verify you are human” checks aimed at visitors. Some of it survived a full change of every password.

The usual security plugins had not stopped it. So we wrote our own. Guardian Shield Lite starts from one idea: an attacker’s code should not be able to run on your site in the first place. Every lesson from those incidents became a rule in the plugin, and every rule has a test that must pass before a new version ships.

What it does

Six layers between an attacker and your site.

  • Code stays locked

    Installing or uploading plugins and themes, the file editors and code uploads are blocked by default. Changes happen in short unlock windows that are time-limited, limited to what the job needs, recorded and reported.

  • Nothing new runs unapproved

    Must-use plugins and drop-ins, the places attackers like to hide, are zero trust. A file runs only after it is approved by name and fingerprint, and a changed file goes back for review.

  • Malware removed, evidence first

    Only exact, confirmed malware is removed, and only after a protected copy has been saved. If the copy fails, nothing is deleted. Anything that merely looks suspicious is reported to a person, never deleted.

  • Admin accounts guarded

    New administrators and promotions are blocked while the site is locked, unapproved administrators are demoted, and known malicious accounts are removed. Logins from new places are reported, XML-RPC is closed and new application passwords are blocked or reported.

  • Files checked against the source

    WordPress core files are compared with the official checksums, and plugins from wordpress.org with their official checksums every 12 hours. Sensitive files such as wp-config.php and .htaccess are watched against a trusted baseline.

  • Back doors kept shut

    Application passwords, WooCommerce API keys and webhooks are listed and every change is reported, with webhooks to known data-theft services flagged. After a removal, Guardian writes an incident report: when the file arrived, which requests came in around it, and which access survives a password change.

How it works

Lock. Watch. Remove. Report.

  1. LockCode changes are closed until someone with the right access opens a short, recorded window for the job.
  2. WatchEvery 15 minutes Guardian checks the site, and a full scan of every file runs in steps, riskiest folders first, so big sites are covered completely.
  3. RemoveConfirmed malware, malicious accounts and injected script tags are removed at once, each one saved as evidence first.
  4. ReportOnly what a person must act on is emailed straight away; everything else goes into a daily digest and the 30-day report.

Guardian Hub

Every site, one screen, watched by us.

Every site running Guardian reports to our hub. We see each site’s status, its last full scan, files waiting for approval and anything that needs a person, all on one screen.

  • Every front page is checked every 5 minutes for WordPress’s critical-error page, printed PHP errors and server errors.
  • A site that stops reporting is marked on the dashboard and listed in the daily digest.
  • A separate watchdog runs from the server’s own scheduler, outside WordPress, with its own baseline kept outside the website folder.
  • Unlocks from the hub are signed, time-limited and recorded, like every other unlock.

Built to be trusted

A security plugin should never be the weak spot.

  • Signed and pulled, never pushed

    Sites fetch new signatures every 6 hours and updates from the hub. Everything the hub publishes is signed with Ed25519 and checked before it is used; the hub never pushes code to a site.

  • Nothing lost between versions

    A release is built only when every protection of the one before is still in it, and every automated test suite passes. A fix shipped once cannot quietly disappear.

  • Built not to break your site

    Every check that runs on a visitor’s request is wrapped so that a problem inside Guardian does not break the page. When a PHP fatal error happens on a page Guardian can see, it is emailed at once with its file and line.

  • Quiet on purpose

    Guardian emails only what a person must act on now. Routine events are recorded for the report instead, so a real alert is never lost in noise.

For site owners

Know exactly what happened, in plain English.

From the Guardian page, a site owner can download a PDF report of the last 30 days: what was found, what Guardian fixed, and what still needs attention. It shows only activity that was actually recorded, and when the report is made, Guardian checks each earlier finding against the site again, so something that is gone is listed as resolved.

If an owner is ever locked out while working on their own site, the Guardian page can email a step-by-step unlock guide to an administrator address registered for that site.

Honest limits

What Guardian does not pretend to do.

  • It cannot see every crash from inside

    A plugin cannot catch an error in a WordPress core file that loads before plugins do. That is why the hub checks every front page from the outside.

  • It does not guess

    Broad “looks suspicious” rules only raise an alert. Deleting is reserved for exact, confirmed malware, so nothing legitimate is removed by mistake.

  • It is not a backup

    Guardian keeps evidence of what it removes, not a copy of your site. Keep regular backups alongside it.

How to get it

Included when we look after your site.

Guardian Shield Lite is not sold as a download. It comes with our website security and maintenance services: we install it, set it up for your site, connect it to the hub and act on what it reports. If your site has already been attacked, we start with a malware cleanup and leave Guardian in place to keep it clean.

Ask about Guardian

What Guardian caught on client sites

In Order to Succeed
  • Service business
  • WordPress
  • Website security

Hidden admin powers, a fake Cloudflare redirect and a backdoor, removed by Guardian

Challenge
Customer accounts had been given administrator powers in secret, a script sent visitors to a fake Cloudflare check page, and a backdoor was hidden in a theme file.
Result
All three threats removed automatically. The backdoor, planted in November 2025, was found and removed on 9 September 2026 during a regular scan.
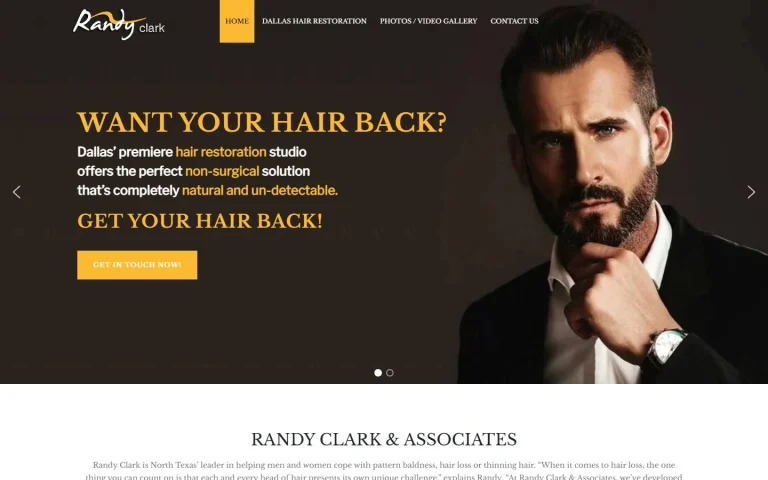
Randy Clark & Associates
  • Service business
  • WordPress
  • Speed optimization

Speed work, a rebuild and a malware cleanup for a hair replacement studio

Challenge
In September 2021 the studio's home page scored 13 out of 100 on Google PageSpeed mobile. The site also needed more and better images: the before and after photos were very low resolution.
Result
Google PageSpeed mobile went from 13 to 97 in September 2021, the rebuilt site went live on 25 May 2023, about seven weeks after kickoff, and Guardian Shield Lite removed the fake Cloudflare malware.

Guardian Shield Lite is developed by Codiffy under the direction of our Security Lead, Muhammad Haroon Ur Rasheed. How Codiffy approaches security

Questions about Guardian Shield Lite.

What is Guardian Shield Lite?

The WordPress security plugin Codiffy built after investigating and cleaning up real attacks in 2026. It keeps code changes locked, removes exact known malware after saving evidence, guards administrator accounts and reports every site to the Guardian hub.

How is it different from other security plugins?

It starts from zero trust. Code changes stay locked, new files in the places attackers hide must be approved before they run, and removal is limited to exact, confirmed malware with a protected copy saved first. Every site also reports to a hub we watch.

Can Guardian delete something by mistake?

It is built not to. Only exact matches of confirmed malware are removed, a protected copy is saved first, and the removal is cancelled if that copy fails. Anything that only looks suspicious is reported to a person.

How are plugins updated while the site is locked?

In short, time-limited unlock windows that are limited to the job, recorded and reported. When we look after your site, we handle updates as part of maintenance.

Does it work with WooCommerce?

Yes. Guardian runs on WordPress with or without WooCommerce, and also watches WooCommerce API keys and webhooks for changes.

Can I buy Guardian Shield Lite?

Not as a download. It comes with Codiffy website security and maintenance services: we install it, set it up, connect it to the hub and act on what it reports.

Does Guardian replace backups?

No. Guardian keeps evidence of what it removes, not a copy of your site. Keep regular backups alongside it.

Put Guardian on your site.

Guardian Shield Lite comes with our website security and maintenance plans: we install it, set it up and watch it for you. Book a free 30-minute call and we will look at your site.

Book my free call
Free call, no obligationBook my call