Security at Codiffy
Codiffy builds, looks after and protects WordPress and WooCommerce websites. Who leads our security work, how we keep it defensive and authorized, and Guardian Shield Lite, the security plugin we develop.
Security leadership
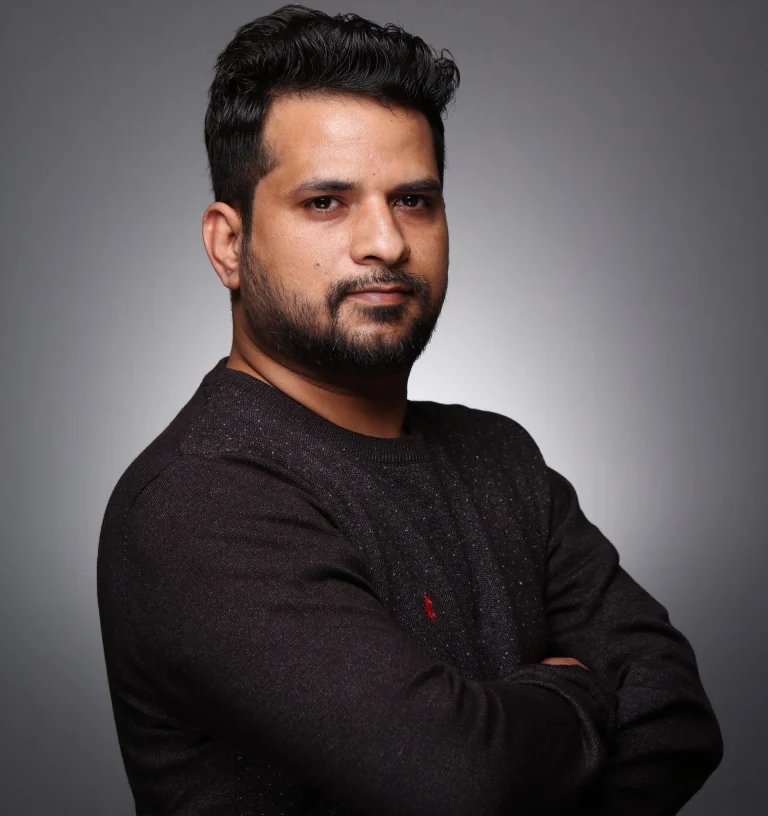
Muhammad Haroon Ur Rasheed
Founder & CEO, Codiffy
Security Lead
Security leadership
Muhammad Haroon Ur Rasheed, Founder & CEO of Codiffy, is the company's Security Lead. He leads Codiffy's application security and security incident-response work: WordPress and WooCommerce security, vulnerability management, malware remediation, infrastructure hardening, security monitoring, and the direction of Guardian Shield Lite, Codiffy's WordPress security plugin.
He has built with WordPress and WooCommerce for more than 10 years and founded Codiffy in 2018. Read more about him in a message from our founder and on his team profile.
His security responsibilities
- WordPress security
- WooCommerce security
- Application security for the websites, plugins and integrations we build
- Security incident response
- Vulnerability identification and remediation
- Malware detection and remediation
- Website and server security hardening
- Authentication and access-control security
- Security monitoring
- Backup and recovery validation
- Security reviews of custom plugins and integrations
- Oversight of Codiffy's internal security tooling
- Oversight and development direction of Guardian Shield Lite
Our security approach
Authorized systems only. Security work performed by Codiffy is limited to Codiffy-owned systems and systems that Codiffy has been explicitly authorized to develop, maintain, administer, assess or protect. Security assessments run only within a scope the owner approves in writing.
Our security work is defensive. It covers seven stages, on the websites we build and the ones we are asked to look after.
Prevention
Keeping WordPress, plugins and themes up to date, removing what a site does not need, and closing the gaps attackers rely on before they are used.
Detection
Watching for known malware, unexpected code, changed files and administrator accounts nobody created.
Monitoring
Continuous checks on the sites we look after, with alerts that reach a person who can act.
Remediation
Removing malware and the way in, with a copy of every malicious file and database entry kept as evidence first.
Hardening
Locking down logins, file permissions, configuration files and the tools a site exposes to the internet.
Recovery
Bringing a compromised site back to a clean, working state and rotating the passwords and keys an attacker could still use.
Validation
Checking afterwards that the infection is gone, the fixes hold and backups can be restored.
Authorized security testing
Codiffy maintains an authorized security-testing function for web applications, WordPress and WooCommerce environments, custom plugins, integrations, and infrastructure where Codiffy owns the systems or has explicit authorization from the system owner.
Every assessment starts with a written scope from the system owner. We test only what that scope covers, and we report the findings in plain words, with the evidence and the fixes in order of importance. Testing is part of our defensive work: its purpose is to find and close weaknesses before they can be used.
A Codiffy security product
Guardian Shield Lite
Guardian Shield Lite is the defensive WordPress and WooCommerce security and monitoring plugin developed by Codiffy. It runs on the WordPress sites we manage, and its development continues under Muhammad Haroon Ur Rasheed's direction.
Its job is to find the security problems that matter, help fix them, and keep alerts quiet unless something needs a person's attention.
Suspicious change detection
New or changed code and settings are flagged as soon as they appear.
WordPress integrity monitoring
Core, theme and plugin files are compared with known good copies.
Malware detection
Known malware is recognized from signatures kept up to date across every protected site.
Indicators of compromise
Files, accounts and settings that match known attacks are identified.
Administrator account monitoring
New administrators and unexpected permission changes are caught and reported.
Website security monitoring
Regular scans, and checks that each site's front page is up and healthy.
Remediation workflows
Confirmed malware is removed only after a copy is saved as evidence.
Security hardening
Site code stays locked, and changes happen in recorded, time-limited windows.
Event prioritization
Urgent findings are emailed at once; routine activity goes into a daily summary.
Central visibility
Every protected site reports to one dashboard that our team watches.
Our security work
The security services we provide for WordPress and WooCommerce websites, always on sites we own or are authorized to work on.
WordPress malware cleanup
Malware, spam redirects, hidden administrators and fake plugins removed, and the way in closed.
Learn moreWordPress incident response
What happened, when and how, found from the files, database and logs, and the site recovered.
Learn moreWooCommerce security
Stores, checkout, customer accounts and logins covered by our security services for WooCommerce sites.
Learn moreCompromised administrator account investigation
Unknown or hidden administrator accounts traced, removed and the access behind them closed.
Learn morePlugin and theme vulnerability remediation
Vulnerable plugins and themes updated, replaced or patched, tested on staging first.
Learn moreWebsite hardening
Outdated software, weak logins and code editable from the dashboard dealt with.
Learn moreServer security hardening
File permissions, configuration file protection and PHP settings checked.
Learn moreFile integrity monitoring
Changed files and new code noticed and reported as they happen.
Learn moreAuthentication security
Logins, passwords, two-factor authentication and administrator access reviewed.
Learn moreSecurity monitoring
Continuous checks with alerts to a person who can act.
Learn morePost-incident validation
Checks after a cleanup that the infection is gone and stays gone.
Learn moreSecurity assessments within an authorized scope
A review of a site you own or are authorized to have tested, within a scope approved in writing.
Learn more
Security is part of how we build and look after websites too: our WordPress development, WooCommerce development and maintenance and support work follows the same approach. More about the company on About Codiffy.
Questions about security at Codiffy.
Who leads security at Codiffy?
Muhammad Haroon Ur Rasheed, Founder & CEO of Codiffy, is the company's Security Lead. He leads Codiffy's application security and security incident-response work and directs the development of Guardian Shield Lite.
Which systems does Codiffy’s security work cover?
Only Codiffy's own systems and systems Codiffy has been explicitly authorized to develop, maintain, administer, assess or protect. Security assessments run only within a scope the owner approves in writing.
What is Guardian Shield Lite?
The defensive WordPress and WooCommerce security and monitoring plugin developed by Codiffy. It flags suspicious changes and known malware, watches administrator accounts, removes confirmed malware only after keeping a copy as evidence, and reports every protected site to one dashboard our team watches.
Can Codiffy help with a hacked WordPress or WooCommerce site?
Yes. We remove the malware and the way in, keep evidence first, rotate the passwords and keys an attacker could still use, and check afterwards that the site is clean. Contact us and choose “An urgent problem” in the form.
How do I report a security issue with a website Codiffy manages?
Use the contact form and choose “An urgent problem (site down, hacked, checkout broken)”, or email support@codiffy.com. Tell us which website it is and what you saw.
Security questions or incident assistance?
If you believe a website managed by Codiffy has a security issue, or you need help with a compromised WordPress or WooCommerce website, contact our team. In the form, choose “An urgent problem” so it reaches the right people quickly.